掃描 GitHub 上 8 個新近更新的 Next.js + Supabase AI 專案:5 個獲 F,發現 288 項安全問題
I scanned 8 newly shipped Next.js + Supabase AI repos on GitHub - 5 scored an F (288 security findings)
一次針對 GitHub 上 8 個新近更新的 Next.js、Supabase 和 OpenAI 專案的掃描,發現 6 個有實際安全漏洞,5 個獲 F,合共 выяв出 288 項安全問題。作者亦製作了三款免費開源工具 Vibe-Shield、Unslop 和 Ghost-QA,供 Claude Code 和 Cursor 使用,並可在本機執行。

Today I ran a security scanner across 8 recently updated Next.js + Supabase + OpenAI repositories on GitHub.
The Results:
- 6 out of 8 repos (75%) had real security vulnerabilities.
- 5 out of 8 scored a Grade F.
- 288 total security issues across just 8 projects.
The Top 3 Mistakes AI Coding Agents Make:
-
No Row Level Security (RLS): AI writes
CREATE TABLEin Supabase migrations, but forgetsENABLE ROW LEVEL SECURITY—or silences errors withUSING (true). Anyone can dump or wipe the database from Chrome DevTools usingNEXT_PUBLIC_SUPABASE_ANON_KEY. -
Unprotected API Routes: AI creates Next.js
POSTandDELETEroutes with zero session check, or trustsuserIdfromreq.json()instead of the server session. -
Leaked Client Keys: Putting secret keys into
NEXT_PUBLIC_orVITE_variables.
Test Your Own Repo in 3 Seconds
I built three free, open-source tools for Claude Code and Cursor that run 100% locally on your machine:
1. Vibe-Shield v2.0 (85-Rule Security Scanner & Attack-Surface Mapper)
npx -y @vibefoundry/vibe-shield@latest scan .
 avivgerz-hue
/
vibe-shield
60-rule static security scanner, MCP server & skill poisoning auditor for AI-generated codebases (Claude Code, Codex, Cursor).
🛡️ vibe-shield
The security gate for AI-written code.
Your agent ships fast. It also ships NEXT_PUBLIC_SUPABASE_SERVICE_ROLE_KEY, a DELETE route with no session check, and a CREATE TABLE with no Row Level Security — because it was optimising for "it works".
vibe-shield is a static security scanner built for that failure mode, plus an Agent Skill that makes Claude Code, Codex, Cursor and Windsurf audit before they say "done".
npx -y @vibefoundry/vibe-shield scan

v2.0.0: eight defensive vectors
The v2 catalogue covers client exposure; auth and route protection; database/RLS; AI and web sinks; infrastructure; dependency hygiene; secrets and cryptography; and agent/MCP integrity. The new hardening checks include production source maps, insecure JWT settings, explicit and omitted cookie flags, locally absent security headers, container users, lifecycle scripts, lockfiles and weak cryptography. Run rules for the complete catalogue.
The scanner produces a heuristic attack-surface inventory of route methods, observed guard signals…
2. Unslop v2.0 (72-Rule Anti-AI-Slop UI Linter & 10 Design Token Systems)
npx -y unslop-mcp@latest audit ./src
avivgerz-hue
/
unslop
Studio-grade UI design systems, Design DNA extractor & Anti-Slop MCP server for AI coding agents (Claude Code, Codex, Cursor, Windsurf).
unslop v2.0.0
Your agent can write the code. unslop gives it a measurable design engineering protocol.


unslop is a zero-runtime-dependency UI/UX Design Engineering CLI, native MCP Server, and AI Agent Skill. It audits 72 rules across seven design craft pillars, installs ten studio-grade archetypes, extracts Design DNA, exports four token formats, and turns every finding into an exact, prioritized transformation blueprint for JSX/TSX, HTML, Vue, Svelte, CSS, and Tailwind codebases.
Works with Claude Code, OpenAI Codex, Cursor, Windsurf, Cline, and any agent that reads project instructions.
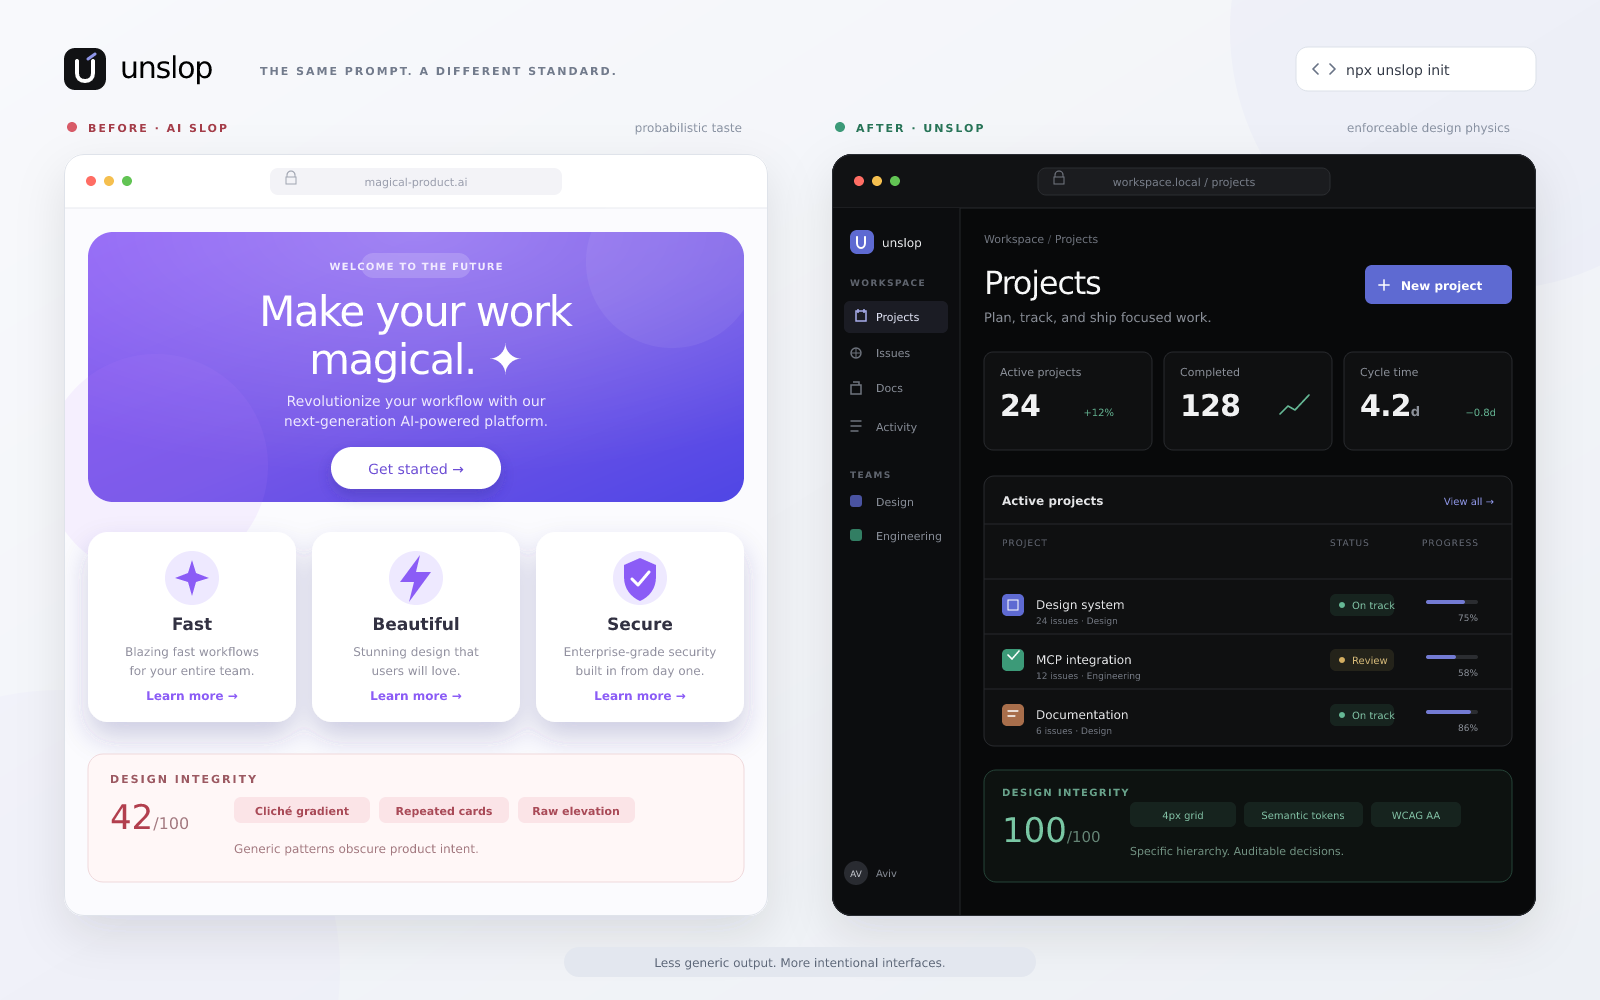
npx -y unslop-mcp init --preset linear-precision
npx -y unslop-mcp audit .
npx -y unslop-mcp refactor-plan . --report UNSLOP-REPORT.md
The result is not a generic prompt. It is a versioned token contract, a Design Craft Score from 0–100, a seven-pillar scorecard, exact before/after translations, and file-level steps your agent can execute in one coherent pass.
v2 at a glance
| Capability | v2 contract |
|---|
…
3. Ghost-QA v2.0 (8-Trap Headless Browser QA for Desktop & Mobile)
npx -y ghost-qa@latest test http://localhost:3000
avivgerz-hue
/
ghost-qa
Autonomous headless browser QA & self-healing verification loop for AI coding agents
👻 ghost-qa
Autonomous headless browser QA & self-healing verification loop for coding agents. v2.0.0 — the 8-Trap Deep Browser Inspection Engine: 3 viewports × light/dark, QA Health Score (A+…F), interactive HTML dashboard, and regression diffing.


Coding agents (Claude Code, Codex, Cursor, Windsurf) write code blind — then declare victory while the actual browser has React hydration errors, broken buttons, 500ing APIs, or mobile layout overflow.
ghost-qa fixes that. One command launches a headless browser against your running app, crawls the live DOM, safely pokes every button, traps runtime/network/layout failures, and hands the agent a structured Self-Healing Bug Report so it fixes its own bugs before telling you it's done.
npx -y ghost-qa test http://localhost:3000No test scripts. No config. No mercy for "it works on my machine".
Prefer running straight from GitHub instead of npm?
npx -y github:avivgerz-hue/ghost-qa test http://localhost:3000works identically — every command in this README accepts either…
If you run the command on your repo, drop your Grade (A+ to F) in the comments!

來源:DEV Community · dev.to