JWT 解碼不等於驗證:初學者的接受檢查清單
Decoding a JWT is not validating it: a beginner’s acceptance checklist
JWT 解碼只會顯示可讀載荷,不能證明其中的聲明已獲驗證;使用聲明授權前,必須按預先訂明的政策驗證 token。檢查政策應涵蓋接受的演算法、發行者、受眾及時間相關聲明。清單依次為解析、按固定政策驗證、驗證聲明,再執行授權。
JWT means JSON Web Token: a format for carrying claims, such as statements about a subject or recipient. Many JWT debugging tools display a readable payload immediately. This is useful for learning the structure, but readable claims have not necessarily been authenticated. Before using a claim to grant access, identify the token type and apply a validation policy designed for that use.
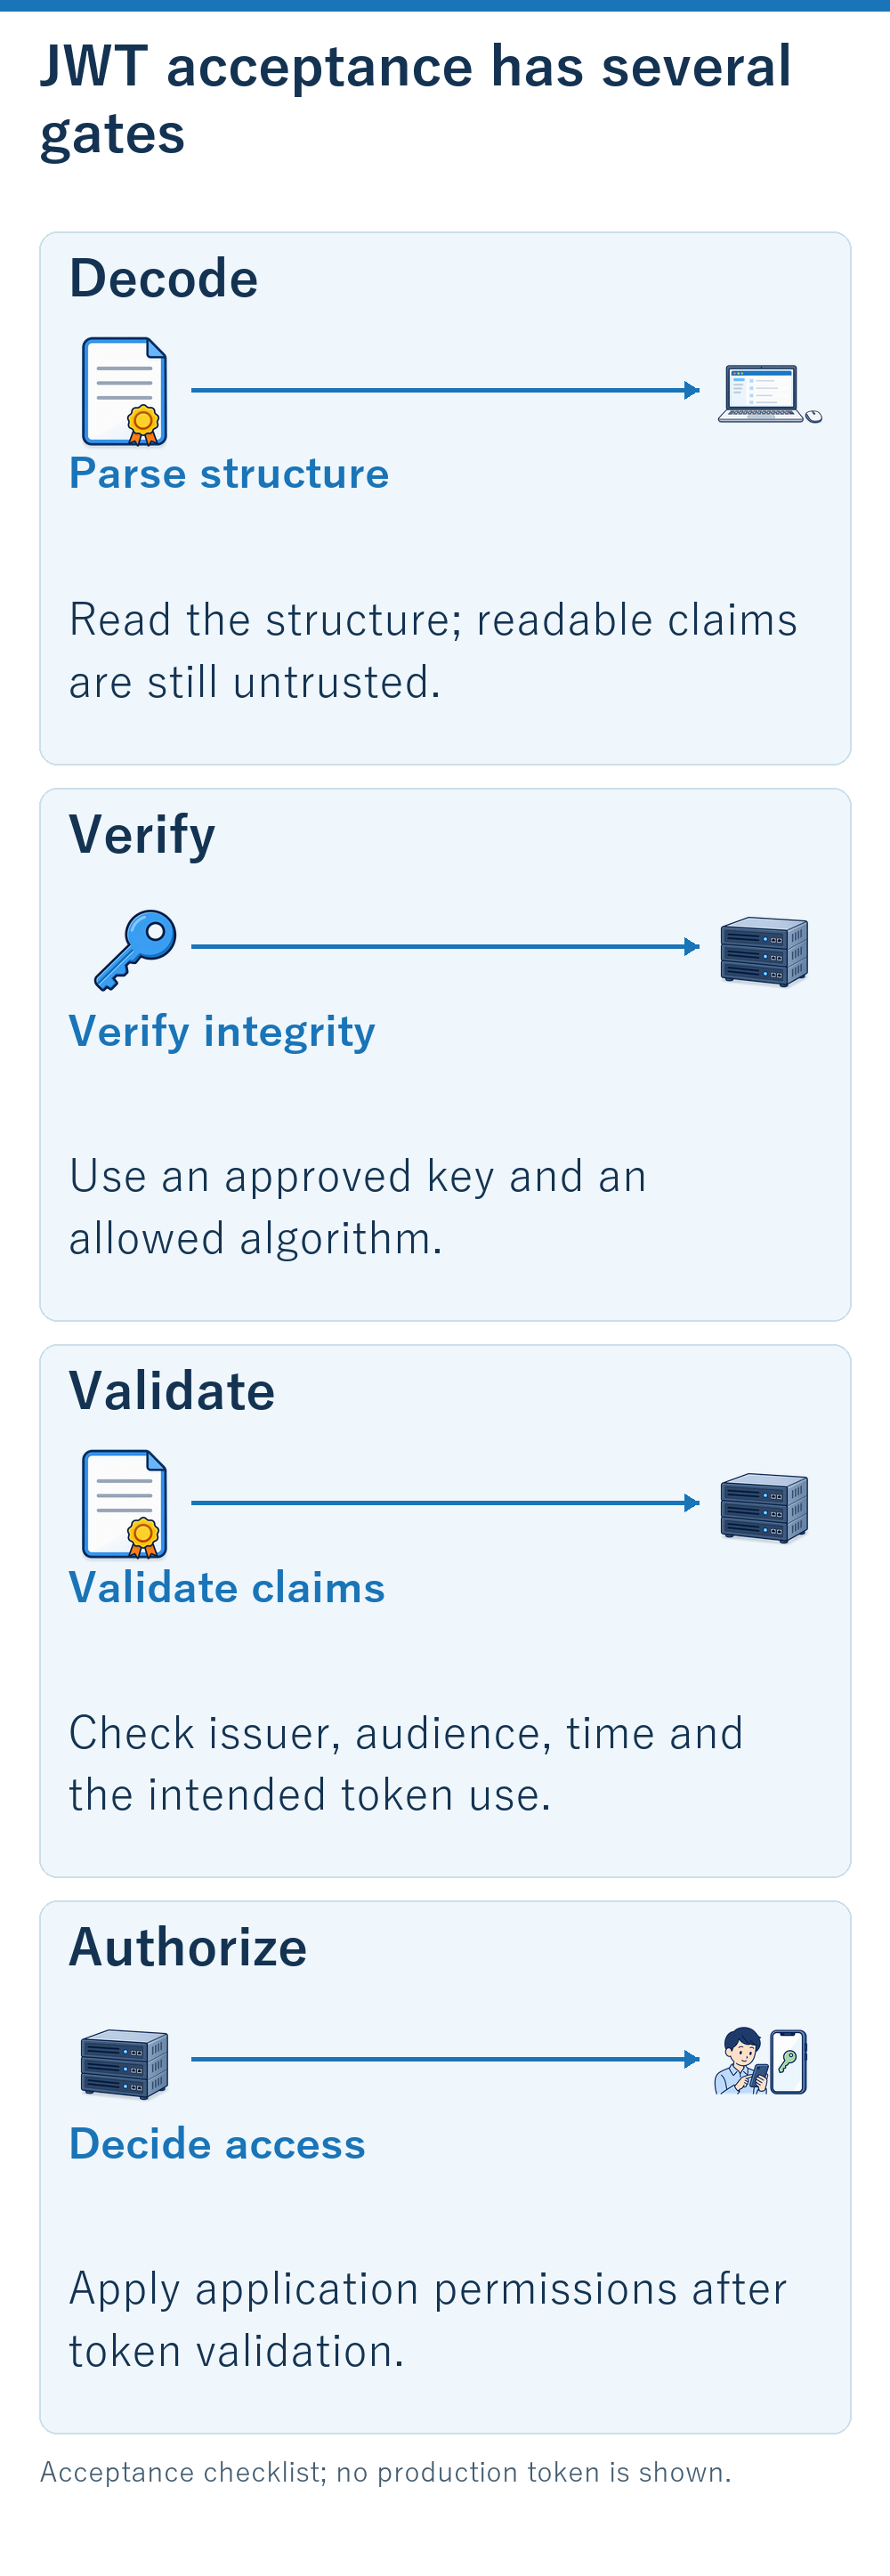
Acceptance checklist; no production token is shown.
Distinguish the envelope
A commonly encountered JWT uses JWS (JSON Web Signature) to protect integrity. Its encoded payload can be readable without a secret. Encryption is a separate mechanism, such as JWE. Do not put sensitive information into a signed token on the assumption that the signature hides it.
Avoid pasting real access tokens into public debugging websites. A bearer token can grant access even when its payload seems uninteresting.
Choose policy before inspecting attacker-controlled fields
The verifier should know which algorithms, issuers and audiences it accepts. Do not let an untrusted token redefine that policy simply by declaring an algorithm or naming a key. Use a maintained library and the framework’s supported integration path.
Successful signature verification is one gate. The application must also decide whether this token was issued for this recipient and this kind of operation.
Check time and intended recipient
Validate required issuer, audience and time-related claims according to the application’s token profile. A token valid for one service may be inappropriate for another. A token intended for one purpose should not silently become acceptable in a different flow.
Write down the small clock tolerance, if any, and why it exists. A large tolerance added to silence failures changes the acceptance policy.
Turn mistakes into test cases
Create tests for a wrong audience, wrong issuer, expired token, unsupported algorithm and a token from a different flow. Use test credentials and synthetic claims, never live user tokens in a public fixture.
The checklist is: parse, verify under fixed policy, validate claims, then apply authorization. The exact order inside a library can differ, but no earlier convenience step should be mistaken for permission to trust the payload.
Primary sources
Further reading on PKI Channel
The following Japanese-language guides add diagrams and operational detail to the questions discussed above.
AI was used for research assistance, writing and illustration. Examples and checklists are explanatory, not reported lab results.
來源:DEV Community · dev.to